Cyber Attack Ignites French Supermarket Fridges to 50C, Causing Fires
Hackers triggered a cyber attack on hundreds of French supermarkets, overheating fridges to 50C and igniting fires, leading to significant food loss.
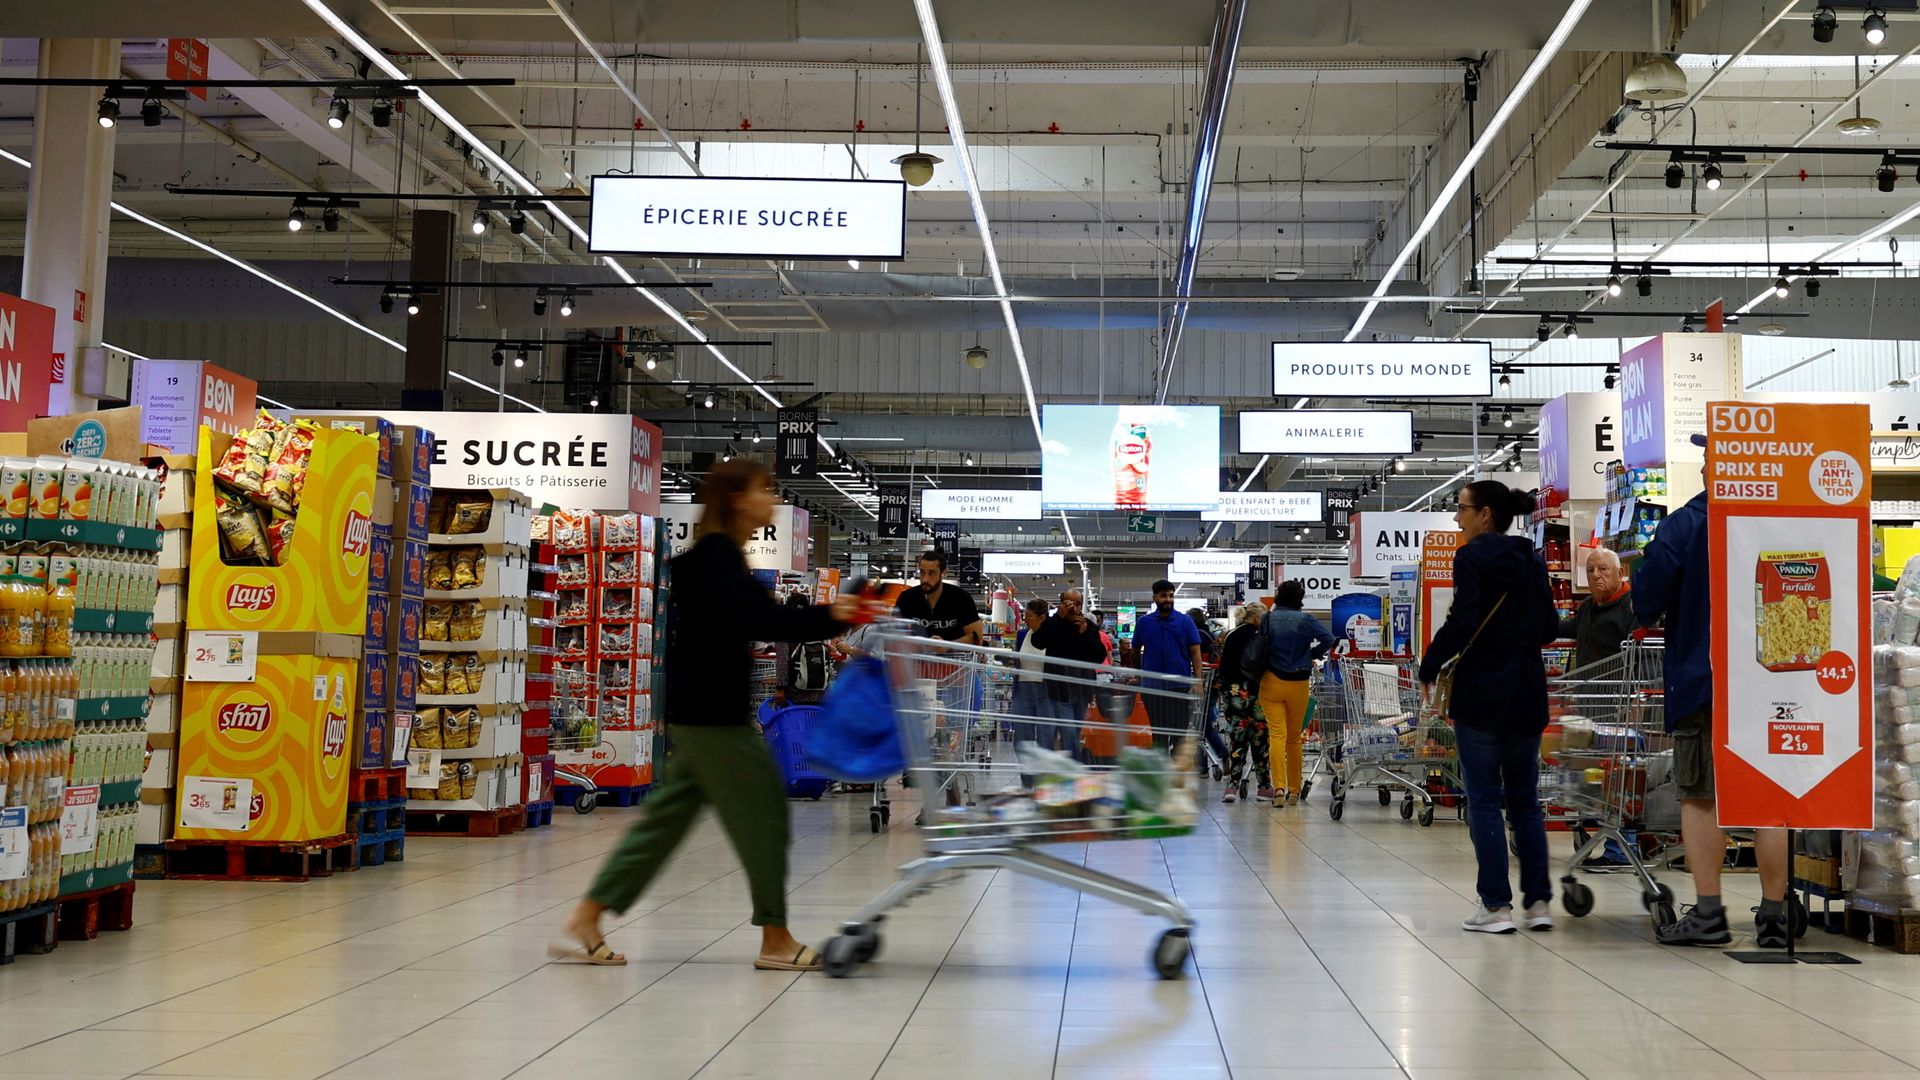
Hundreds of French supermarkets experienced widespread disruption overnight as a sophisticated cyber attack pushed refrigeration units to dangerous temperatures, in some cases reaching 50 degrees Celsius (122 degrees Fahrenheit). The extreme heat generated within the cooling systems reportedly sparked fires in multiple locations, causing significant damage to store infrastructure and leading to substantial food spoilage.
The precise number of affected supermarkets and the full extent of the damage are still being assessed, but initial reports indicate a broad geographical spread across France. The attack targeted the electronic systems that control the temperature and operation of the refrigeration units, a critical component for any food retailer. This incident highlights a new and alarming dimension to cyber threats, moving beyond data theft or system paralysis to direct physical damage.
Eyewitness accounts and preliminary reports from store managers describe scenes of chaos as alarms sounded and smoke began to fill the aisles. Fire services were dispatched to several supermarkets to contain the blazes that originated within or around the compromised refrigeration units. The overheating appears to have been a deliberate act, rather than a malfunction, with hackers allegedly manipulating the control systems remotely.
This coordinated cyber assault raises serious concerns about the security of critical infrastructure within the retail sector. The ability of malicious actors to cause such direct physical damage and economic loss through digital means could have far-reaching implications for supply chains, food safety regulations, and the overall resilience of the food retail industry. Investigations are underway to identify the perpetrators and the methods used.
The motive behind the attack remains unclear, with possibilities ranging from extortion to a demonstration of capability by a sophisticated hacking group. The economic impact is expected to be considerable, not only from the direct costs of repairing damaged equipment and replacing spoiled inventory but also from potential business interruption and reputational damage to the affected supermarket chains.
Experts in cybersecurity are warning that this incident could signal a shift in the tactics of cybercriminals, with an increasing focus on exploiting vulnerabilities that lead to physical consequences. The interconnected nature of modern retail systems, from inventory management to climate control, presents a vast attack surface that may not always be adequately secured against such novel threats.
Retail industry bodies and government agencies are expected to convene in the coming days to discuss the ramifications of this attack and to review existing security protocols. The incident is likely to spur increased investment in cybersecurity measures specifically designed to protect operational technology (OT) within the retail environment.
Questions remain about how the hackers gained access to the supermarket systems and whether similar vulnerabilities exist in other retail networks across Europe and beyond. Authorities are working to trace the origin of the attack and to apprehend those responsible, while supermarkets grapple with the immediate aftermath and the long-term implications for their operational security.
This article was written by AI based on publicly available news reporting. Original reporting by the linked source.